
Introduction
I recently renewed my CompTIA Security+ certification for another three years, keeping it active as required for my work in the federal cybersecurity space. In many federal positions, especially those aligned with DoD 8570/8140 requirements, maintaining a baseline certification like Security+ is essential. While not the toughest certification out there, it serves as a solid foundation in cybersecurity and has been part of my credentialing since I first earned it in 2016.
Overview of the CompTIA Security+ (SY0-701) Exam
The CompTIA Security+ (SY0-701) certification is the latest version of the industry-standard cybersecurity credential, designed to validate essential security skills required for IT professionals. This version emphasizes assessing security risks, applying threat intelligence, managing security operations, and implementing risk mitigation strategies. It ensures candidates can protect systems from modern cyber threats, respond to security incidents, and support an organization's cybersecurity framework.
The SY0-701 exam is structured into five key domains:
- General Security Concepts
Covers fundamental security principles, including confidentiality, integrity, availability (CIA), authentication and authorization models, and essential security frameworks. It also introduces basic cryptographic concepts, security control types, and best practices for maintaining secure environments. - Threats, Vulnerabilities, and Mitigations
Focuses on identifying and analyzing various cyber threats, attack techniques, and vulnerabilities in systems, applications, and networks. It includes topics such as malware, phishing, social engineering, denial-of-service attacks, and risk assessment methodologies to help prevent and mitigate cyber threats effectively. - Security Architecture
Examines secure network and system design, cloud security considerations, endpoint protection, and identity and access management (IAM). This domain ensures candidates understand how to implement security controls across on-premises, cloud, and hybrid environments to protect data and resources. - Security Operations
Addresses key operational security tasks, including monitoring security events, responding to incidents, conducting digital forensics, and implementing security automation. It covers SIEM (Security Information and Event Management), logging, security orchestration, and best practices for maintaining security operations in an organization. - Security Program Management and Oversight
Focuses on governance, compliance, risk management, and security policies. Topics include security frameworks and regulations, business continuity planning, disaster recovery strategies, and the role of security leadership in overseeing an organization's cybersecurity posture.
Each domain ensures that Security+ remains a relevant, vendor-neutral certification for IT and cybersecurity professionals.
For a full breakdown of the exam objectives and additional details, visit: 🔗 CompTIA Security+ (SY0-701) Exam Objectives.
The Renewal Process

Instead of retaking the exam, I renewed through CompTIA's CertMaster CE Security+ course. This self-paced, online training provides an automatic way to extend the certification for another three years.
- Cost: $205 (covered by my employer)
- Eligibility: Must have an active Security+ CE certification from exam SY0-601 or earlier
- Time Commitment: Estimated at 8 to 10 hours, but I completed it in around 6 hours
- CEU Credits: Course completion fulfills all CEU requirements automatically
It's a straightforward process: log in, complete the modules, pass the assessments at 100%, and your certification is renewed. The biggest perk? No need to track CEUs or take another test.
If you're preparing for the CompTIA Security+ (SY0-701) exam, practice questions can be a great way to test your knowledge and identify areas for improvement. CompTIA offers official Security+ (SY0-701) practice questions to help you get familiar with the exam format and reinforce key concepts. You can access them here: 🔗 CompTIA Security+ (SY0-701) Practice Questions.
Wrapping It Up
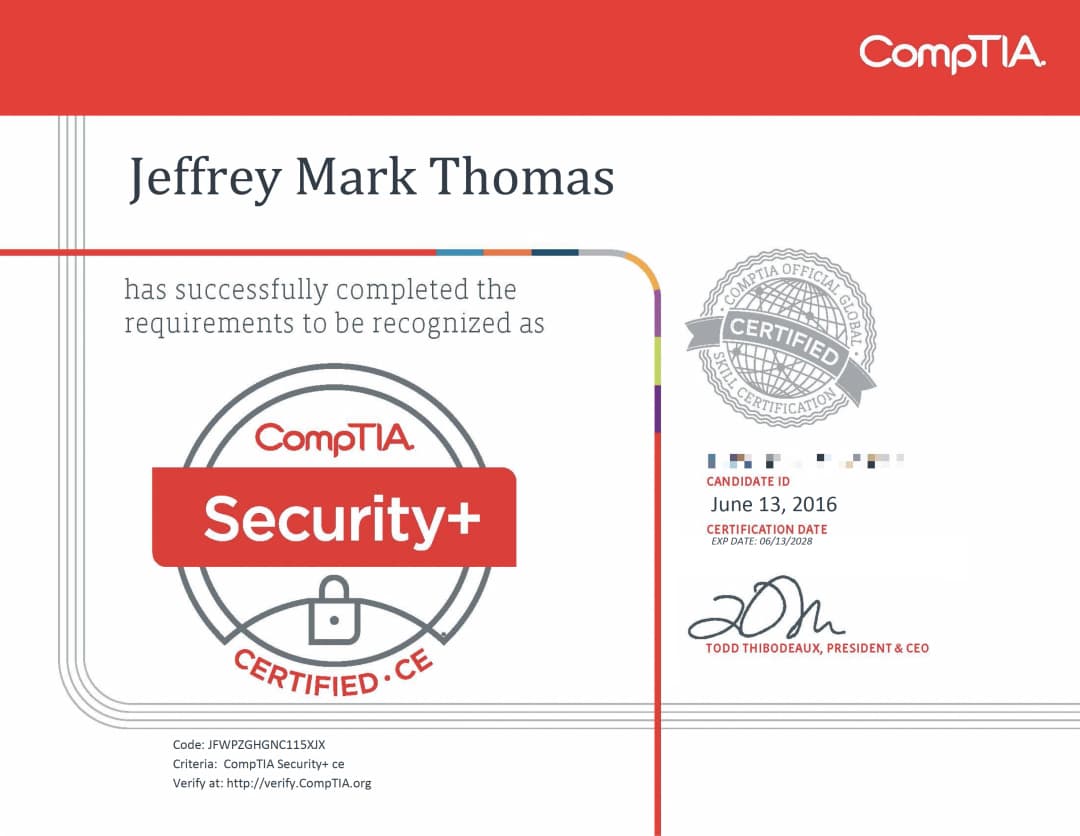
With the renewal complete, my Security+ remains valid for another three years. While this isn't the most exciting credential in my toolkit, it's a necessary one and ensures I stay compliant with federal requirements. If you're looking to renew, the CertMaster CE course is probably the easiest route—just set aside a few hours, knock it out, and move on.
Here's my renewed certificate for proof—onto the next challenge!
Verify My Credential
You can verify my CompTIA Security+ certification through Credly or directly via CompTIA's verification tool using my verification code. To check my credential, visit the Credly verification page or use the CompTIA Certification Verification tool with the code JFWPZGHGNC115XJX. This will confirm the authenticity of my certification and provide additional details about my CompTIA Security+ status.
See the associated LinkedIn post.
Comments
To leave feedback or questions, simply login using your preferred social network. I will read and answer your comments promptly, but please keep in mind that they will be public.